
Docker Products
The platform developers trust, now built for agents
Agent Infrastructure

Sandboxes
Let agents read, write, and run code without risking your machine
Run all your agents in fully isolated environments
No Docker Desktop required, just install and go
brew trust docker/tap && brew install docker/tap/sbx
A real boundary
Every agent gets its own microVM with its own kernel. Your files, your secrets, your machine stay yours.
Start on your laptop, finish in the cloud
Sandboxes start up near instantly. Isolation stops costing you speed in the inner loop. Hand long runs to Docker’s cloud. Same sandbox, same CLI.
Where agents can actually work
A full dev environment, Docker included. Agents build, run, and test like any developer on the team.
Your rules, enforced.
Set network and filesystem limits per sandbox. Denied domains don’t even resolve.
AI Governance
Roll out agents org-wide without losing sight of them
One policy for every machine, no local overrides
Every policy decision logged and streamed to your SIEM

Enforced where agents run.
Agents act in two ways: running code and calling tools. Docker manages both, so policy always holds at execution.
One policy, every machine.
Set network and filesystem rules once. They replace local rules on every sandbox in your org.
Proof for every decision.
Every allow and deny is logged with who, what and which rule, ready for your SIEM.
No bypass with personal accounts.
Require org sign-in through endpoint management, so policy always applies.
MCP Enterprise Gateway
Know every MCP server your agents are running, org-wide
Connect every agent through one gateway you control
Credentials never end up in an agent’s context or a config file

One connection to everything
Agents connect to the Gateway once and reach every tool you’ve approved. One place to see what’s in use, add what’s needed, and revoke what isn’t.
Agents never hold your keys
MCP Enterprise Gateway signs in to each tool and passes credentials only at call time. Agents can use the tool, they never see the key.
Add tools without adding risk
Every server in the MCP Catalog is vetted, signed, and containerized by Docker. New capability for your agents, nothing unknown on your machines.
アプリケーションセキュリティー
Docker Hardened Images
Cut your CVE backlog without changing how you build
Prove what’s in every image you ship
Migrate by changing one line
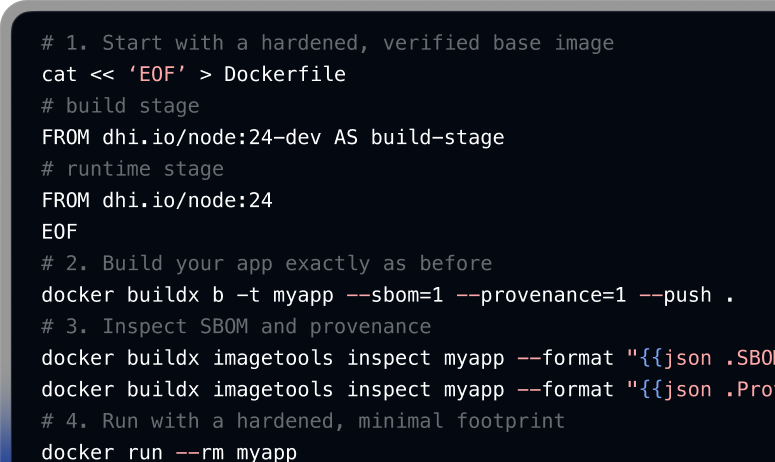
Small on purpose
Hardened Images strip out shells, package managers, and everything else an attacker could use. Less surface, fewer CVEs, quieter scanners.
Kept clean for you
Images stay at near-zero known CVEs, with critical fixes in seven days. Independently assessed by SRLabs.
Evidence built in
Every image ships with a signed SBOM and build provenance. When the auditor asks…show, not tell.
Fixes before you ship
Scout reads your images, flags what’s vulnerable, and surfaces the fix in CI. Remediation moves ahead of release.
アプリケーション開発
Docker Desktop & Docker Hub
Every developer gets the same environment, on any OS
Trusted content one pull away
Managed centrally, from ten developers to tens of thousands
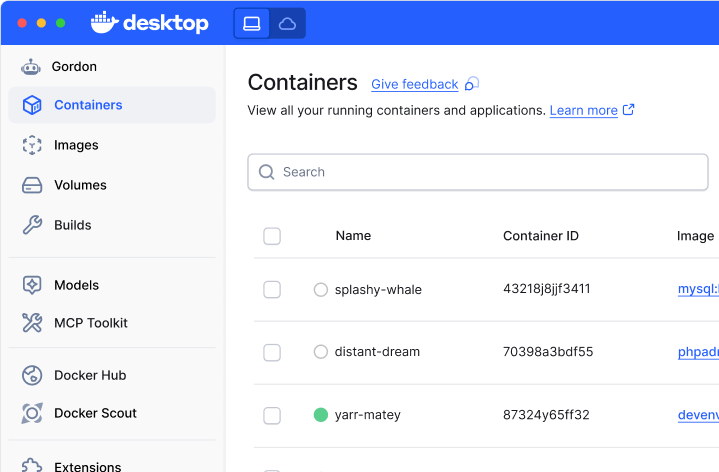
Consistent by default
Desktop puts the same environment on every Mac, Windows, and Linux machine. “Works on my machine” retires.
Start from trust
Hub keeps Official Images and Verified Publisher content one pull away. Teams build on vetted sources, not luck.
Run it like an enterprise
SSO, managed settings, and access controls, administered from one place. The controls your org expects, invisible to developers.
Developers building on Docker
“Docker Sandboxes have the best DX of any local AI coding sandbox I’ve tried.”
“We chose Docker Hardened Images for its alignment with our supply chain security posture, developer tooling compatibility, and Docker’s maturity in this space.”
物語を読む
Walmart’s data science teams build and test with Docker Desktop before anything ships.
物語を読む